
What is the Zones and Conduits Model?
The Zones and Conduits Model is the method from IEC 62443 for dividing an industrial automation system into zones of assets that share common security requirements, and for routing all communication between those zones through controlled conduits. It is a core principle of industrial cybersecurity for factories, water treatment plants, power stations and other OT environments. For each zone and each conduit you set a risk-based target security level, so that you invest in countermeasures where they have the greatest effect. An incident in one zone then stays contained in that zone instead of spreading across the whole plant.
🧠 What are zones and conduits according to IEC 62443?
The terms are defined in IEC 62443-1-1 (terminology and models, 2009) and worked out in IEC 62443-3-2 (security risk assessment for system design, 2020). The technical requirements for each zone and conduit are in IEC 62443-3-3 (2013).
| Term | Description | Examples |
|---|---|---|
| Zone | A grouping of logical or physical assets that share common security requirements | PLC zone, SCADA/HMI zone, SIS zone, MES zone |
| Conduit | A logical grouping of communication channels that connects two or more zones and shares common security requirements | SCADA zone ↔ DMZ link, remote access connection |
| SuC | System under Consideration: the defined system you assess, with its perimeter and access points | One production site or one process unit |
| SL | Security level 0 to 4, indicating which type of attacker a zone or conduit must withstand | SL-T 2 for a control zone |
Communication within a zone does not need a conduit; anything that crosses a zone boundary does. A conduit can be a single cable or connection, but also several channels that share the same security requirements. Zones may be nested: a critical sub-zone can have stricter requirements than the zone around it.
🎯 Why divide an OT network into zones and conduits?
- Segmentation limits the damage - malware or an attacker that reaches one zone cannot spread unchecked (lateral movement).
- Security policy per zone - countermeasures are matched to risk and function, instead of one heavy regime for the entire network.
- Control over data flows - only named, necessary communication may cross a zone boundary, which prevents unwanted access and data leaks.
- Spending in the right place - a safety system gets more protection than a canteen information display.
- Demonstrability - zone and conduit drawings show auditors and regulators how you manage your risks.
The model is therefore the practical form of defence in depth in OT: multiple layers, each with its own boundary.
🔧 How do you define zones and conduits under IEC 62443-3-2?
IEC 62443-3-2 describes a work process of seven Zone and Conduit Requirements (ZCRs). The standard is performance-based: it tells you what to do, not which method to use.
| Step | Requirement | Output |
|---|---|---|
| ZCR 1 | Identify the System under Consideration, including its perimeter and access points | Architecture drawing and asset inventory |
| ZCR 2 | Perform an initial cybersecurity risk assessment (worst case if compromised) | Initial view of the risk |
| ZCR 3 | Partition the SuC into zones and conduits | Initial zone and conduit diagram |
| ZCR 4 | Compare the initial risk with the tolerable risk | Decision on whether a detailed assessment is needed |
| ZCR 5 | Perform a detailed risk assessment per zone and conduit and determine the SL-T | Residual risk and SL-T per zone and conduit |
| ZCR 6 | Document requirements, assumptions and constraints | Cyber Security Requirements Specification (CSRS) |
| ZCR 7 | Obtain asset owner approval | Formal acceptance |
Under ZCR 3 the standard prescribes a number of fixed separations:
- Business and IACS assets separated - office systems such as ERP do not belong in the same zone as IACS assets.
- Safety-related assets separated - a SIS gets its own zone; if that is not possible, the entire zone is treated as safety-related.
- Temporarily connected devices separated - service engineers’ laptops and portable engineering stations.
- Wireless devices separated - Wifi and WirelessHART equipment.
- Devices connected via external networks separated - for example equipment that comes in over the internet or a supplier network.
ZCR 5 consists of thirteen sub-steps: identifying threats and vulnerabilities, determining consequences and likelihood, setting the SL-T, taking existing countermeasures into account and comparing residual risk with tolerable risk. Many organisations use a cyber PHA in HAZOP style for this, so that process safety and cyber risk come together in a single analysis.
📊 What do SL-T, SL-C and SL-A mean?
Every zone and every conduit receives a target security level (SL-T). Formally this is a vector of seven values, one per foundational requirement (FR 1 to FR 7, ranging from identification and authentication control to resource availability).
| Level | Protects against | Typical threat |
|---|---|---|
| SL 1 | Casual or coincidental violation | Operator error, wrongly connected laptop |
| SL 2 | Intentional violation using simple means | Generic malware, low skills and resources |
| SL 3 | Intentional violation using sophisticated means | Criminals with OT knowledge and targeted tools |
| SL 4 | Sophisticated attack with extended resources | Nation-state actors with ample time and budget |
- SL-T (target) - the level the risk assessment requires for a zone or conduit.
- SL-C (capability) - the level a component or system can reach when properly configured; vendors demonstrate this through certification against IEC 62443-4-2 (components) or IEC 62443-3-3 (systems).
- SL-A (achieved) - the level actually achieved in practice.
The goal is for SL-A to be at least equal to SL-T. A component with SL-C 3 does not deliver SL-A 3 if default passwords remain in place or the zone boundary is bridged.
🔐 What requirements must a conduit meet?
In IEC 62443-3-3, zone protection falls under FR 5, Restricted Data Flow: SR 5.1 (network segmentation), SR 5.2 (zone boundary protection), SR 5.3 (restrictions on general-purpose person-to-person communication such as email) and SR 5.4 (application partitioning). Which security countermeasures a conduit needs follows from its SL-T. Commonly used measures:
- Firewall or industrial firewall - with a default deny rule set and only named ports and protocols
- Data diodes - one-way communication where data only needs to flow outwards
- Encryption (VPN, TLS) - especially for conduits that run over shared or external networks
- Authentication and authorisation - for example via a jump server in the IDMZ for administrative access
- Monitoring and Logging - visibility of what actually crosses the conduit
- Protocol filtering - for example allowing only read-only Modbus TCP function codes
🏭 What does a zone model for a plant look like?
A simplified example for a medium-sized process plant. The SL-T values are illustrative: in practice they follow from your own risk assessment.
| Zone | Assets | Typical SL-T |
|---|---|---|
| Enterprise (outside SuC) | ERP, email, office workstations | n/a (IT policy) |
| IDMZ | Replica historian, patch server, jump server | 2–3 |
| Site operations | MES, historian, OT domain controller | 2 |
| Supervisory | SCADA servers, HMIs, engineering stations | 2–3 |
| Basic control | PLCs, Remote IO, variable frequency drives | 2–3 |
| Safety | SIS, safety PLCs | 3 |
| Temporary / external | Service laptops, supplier access | 2 |
| Conduit | Between | Permitted traffic |
|---|---|---|
| C1 | Enterprise ↔ IDMZ | Reports and replication, no direct OT access |
| C2 | IDMZ ↔ Site operations | Historian replication, administration via jump server |
| C3 | Supervisory ↔ Basic control | Only the required industrial protocols to known PLCs |
| C4 | Basic control ↔ Safety | Read-only status data, writes only via a fixed engineering procedure |
| C5 | Site operations ↔ Supervisory | Historian data collection and MES orders, only the protocols that are needed |
Note that there is no direct conduit between Enterprise and Basic control: all traffic crosses at least two zone boundaries.
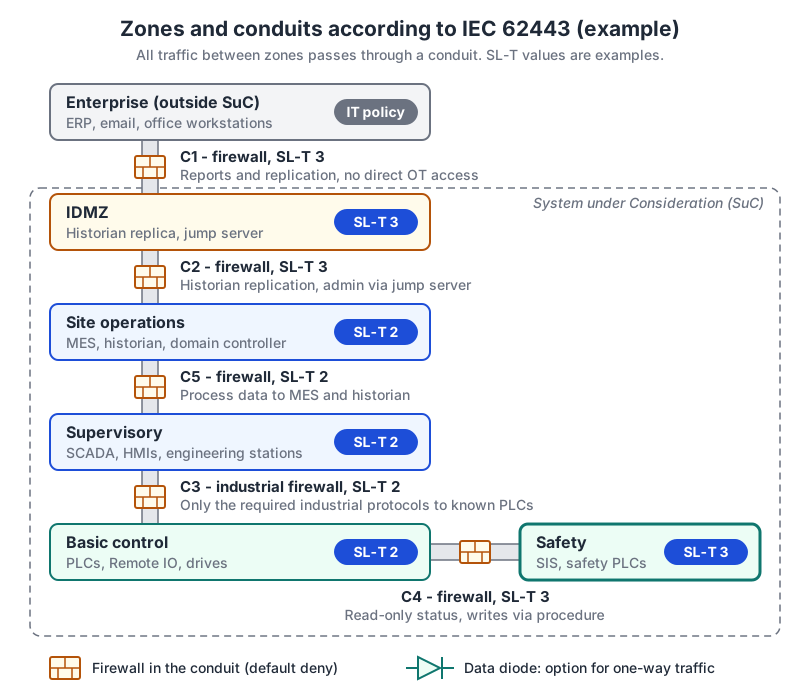
Figure: example zones and conduits model; the SL-T values are illustrative.
🔄 How does the model relate to the Purdue Model?
The Purdue Model describes functional layers, from sensors at Level 0 to ERP at Level 4. The Zones and Conduits Model describes how you group those layers by risk and let them communicate. The reference model in IEC 62443-1-1 is derived from Purdue, which is why zones often coincide with levels in practice.
Even so, a zone is not a synonym for a Purdue level. Levels 1 and 2 (PLCs and SCADA) can form a single zone if they share the same requirements, while the SIS at the same level gets a zone of its own. Conversely, a single production line can form a vertical zone spanning several levels. See also zoned architecture.
⚠️ What are the most common mistakes?
- Equating zones with VLANs - a VLAN without a filtered boundary is not a conduit.
- One flat OT zone - everything behind a single firewall gives lateral movement free rein inside OT.
- Forgotten conduits - supplier access via 4G routers, USB sticks or dual-homed workstations bypass the drawing.
- No SL-T recorded - without a target level you cannot test whether countermeasures are sufficient.
- Model not kept up to date - after extensions the drawing no longer matches reality.
❓ Frequently asked questions
Is a zone the same as a VLAN?
No, a zone is a group of assets with common security requirements, whereas a VLAN is a technical way of separating network traffic. A VLAN can help implement a zone, but a controlled conduit only exists once a firewall or filtering is applied at the zone boundary.
How many zones does an industrial plant need?
The number of zones follows from the risk assessment under IEC 62443-3-2, not from a fixed figure. In practice a medium-sized plant often ends up with five to ten zones, with at least separate zones for business, the IDMZ, control, safety systems and temporary or external access.
Does every conduit need a firewall?
Not every conduit requires a firewall; the necessary countermeasures follow from the conduit’s SL-T. IEC 62443-3-3 does require every zone boundary to be monitored and restricted, and in practice a firewall or data diode is almost always needed on conduits between IT and OT.
Who draws up the zone and conduit model?
The asset owner, the organisation that owns and operates the plant, is ultimately responsible and approves the model in ZCR 7 of IEC 62443-3-2. It is usually developed together with the system integrator, process safety specialists and the OT security team.
Is the Zones and Conduits Model mandatory under NIS2?
NIS2 and the Dutch Cyberbeveiligingswet, which entered into force on 15 August 2026, do not prescribe the model literally. They do require appropriate, risk-based measures, and for OT environments zoning according to IEC 62443 is the most widely used way to demonstrate them.
How often should you review the zone model?
You review the zone and conduit model at every significant change, such as a new production line, additional remote access or a new link to IT, and periodically according to your own policy. This keeps the zone drawings, SL-Ts and firewall rules aligned with the actual installation.
📌 In summary
The Zones and Conduits Model from IEC 62443 divides an OT environment into zones with common security requirements and routes all communication between them through controlled conduits with a risk-based target level (SL-T). Together with the Purdue Model it forms the basis of a secure OT architecture, but it only delivers real protection when it is grounded in the IEC 62443-3-2 steps, implemented with countermeasures from IEC 62443-3-3 and kept up to date.