
What is Defense in Depth?
Defense in Depth is a security strategy in which an organisation places multiple, mutually independent layers of security controls one behind the other, so that an attack that breaks through one layer is still stopped, slowed down or detected by the next. The starting assumption is that every individual control will eventually fail: through a configuration error, an unknown vulnerability or a user who clicks the wrong link. In industrial automation, where availability and physical safety come first, Defense in Depth is the guiding principle behind virtually every OT security standard, from IEC 62443 to NIST SP 800-82.
🧠 Where does Defense in Depth come from?
The term comes from military strategy. Instead of staking everything on a single line of defence, a defender sets up several lines one behind the other. Each line slows the attacker down and costs them resources, while the defender gains time to see the attack coming and to respond. Nuclear safety has also used the principle for decades: several independent barriers between the radioactive material and the environment.
In information security, the concept became widely known through the US NSA. Its paper Defense in Depth: A practical strategy for achieving Information Assurance (2004) stressed three pillars:
- People - awareness, training, roles and responsibilities
- Technology - security controls at multiple places in the network, with different mechanisms per layer
- Operations - management, monitoring and the processes to protect, detect and react
That split between people, process and technology is still the core of the idea. NIST SP 800-82 Rev. 3 describes Defense in Depth as a strategy that integrates people, technology and operational capabilities, with the aim of preventing single points of failure in the defences. A related picture from safety science is the Swiss cheese model: every layer has holes, but an incident only happens when the holes in all layers line up.
🧱 Which layers make up Defense in Depth?
There is no single, universal breakdown, but most models are very similar. The table below combines the common layers with typical controls in an IT/OT environment:
| Layer | Purpose | Example controls |
|---|---|---|
| Policy and governance | Set direction, risks and responsibilities | Security policy, risk assessment, ISO 27001, IEC 62443-2-1, security awareness |
| Physical | Prevent unauthorised access to sites and equipment | Access control, locks, CCTV, locked cabinets and server rooms |
| Perimeter | Control traffic between IT, the internet and OT | Firewall, DMZ / IDMZ, data diode, remote access via a Jump Server with MFA |
| Network | Limit attacks inside the network | Network segmentation, VLANs with filtering, zones and conduits model |
| Host / device | Make the systems themselves hard to attack | Hardening, patch management, Antivirus, application whitelisting |
| Application and access | Allow only authorised users and functions | Least privilege, role-based access, separate OT accounts |
| Data | Protect the confidentiality and integrity of data | Encryption, integrity checks, read-only copies of historian data |
| Monitoring and response | Detect attacks and limit the damage | SIEM, IDS/IPS, logging, Incident Response, backup and recovery |
What matters is not the number of layers but their independence. IEC 62443-4-1 states that each layer should be autonomous and should not rely on the same functionality or share the same failure modes as the other layers. Two firewalls of the same type with the same rules therefore amount to just one layer.
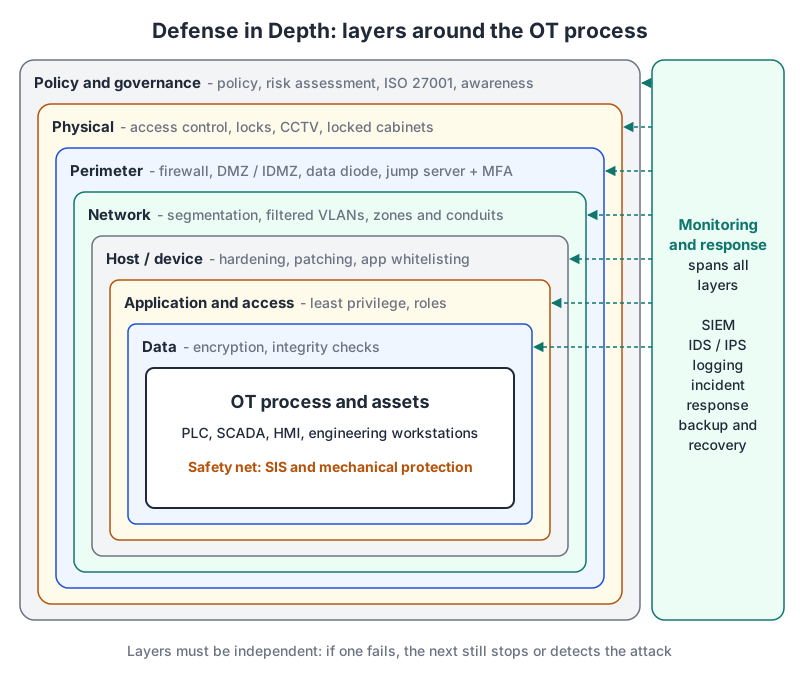
Figure: the layers of Defense in Depth around the OT process; monitoring and response run through every layer.
🏭 How do IEC 62443 and NIST SP 800-82 apply Defense in Depth in OT?
In ICS and SCADA environments, Defense in Depth matters even more than in office IT. Many systems are outdated and cannot be patched, suppliers need temporary access, field equipment is physically reachable, and IT and OT are becoming ever more intertwined. A single control is therefore never enough.
| Framework | How Defense in Depth appears |
|---|---|
| NIST SP 800-82 Rev. 3 (September 2023) | Five layers: 1 Security Management, 2 Physical Security, 3 Network Security, 4 Hardware Security, 5 Software Security. Layer 1 should be in place first. |
| CISA Recommended Practice (September 2016) | Nine elements, from risk management and network architecture to host security, monitoring, vendor management and the human element |
| IEC 62443 | Zones and conduits with a target Security Level per zone (IEC 62443-3-2), system requirements per level (IEC 62443-3-3) |
| IEC 62443-4-1 (2018) | Suppliers must apply Defense in Depth in product design (requirement SD-2) and document which controls they expect in the environment (SG-2) |
IEC 62443 makes Defense in Depth concrete through the zones and conduits model. Systems with similar security requirements are grouped into a zone, and all traffic between zones passes through a controlled conduit. An attacker who gets into one zone is therefore not yet in the next. NIST SP 800-82 also lists concrete controls, such as a DMZ between the business network and OT, MFA for remote access, separate accounts for OT and corporate IT, and a design that degrades gracefully to manual operation during failures instead of stopping abruptly.
🔧 What does a layered OT architecture look like?
A widely used structure follows the Purdue Model. In this example, an attacker who wants to reach a PLC from the internet has to get through seven successive layers:
| Attacker’s step | Layer that stops them |
|---|---|
| Phishing email to an office employee | Email filtering, awareness training, endpoint protection on IT |
| From the office network to OT | IT/OT firewall and a DMZ: no direct traffic between office and OT |
| Logging in to an OT system | Jump Server in the DMZ with MFA, separate OT accounts and session logging |
| Moving laterally within OT | Segmentation into cells and zones, only permitted industrial protocols between zones |
| Running malicious software | Application whitelisting and hardening on HMIs and engineering workstations |
| Staying unnoticed | Passive OT network monitoring (IDS) and a SIEM with OT-specific use cases |
| Causing physical damage | An independent SIS and mechanical protection such as pressure relief valves |
The office network does not pull data such as production figures directly from OT. A historian in OT replicates it to a copy in the DMZ, optionally through a data diode, and users only read that copy. The last layer is not IT at all: a safety instrumented system and mechanical protection prevent a hazardous situation even if every digital layer fails.
🔄 What is the difference between Defense in Depth and Zero Trust?
Zero Trust and Defense in Depth are not mutually exclusive, but they put the emphasis in different places:
- Defense in Depth places layers around the valuable systems. A network zone is often treated as relatively trustworthy once someone has passed its boundary.
- Zero Trust, described in NIST SP 800-207 (2020), trusts no connection on the basis of network location. Every access request is checked again for identity, device and context.
In practice, Zero Trust is a way to strengthen the network and access layers within Defense in Depth. NIST SP 800-82 Rev. 3 also lists zero trust as a building block within the network layer. In OT there is a caveat: many PLCs and field devices do not support modern authentication. There, segmentation, conduits and monitoring remain the most important layers.
🔐 What are the most common mistakes?
- A single hard shell - a strong firewall towards the internet, but a flat network behind it in which every system can reach every other system. After one successful phishing attack or an infected USB stick, everything is exposed.
- VLANs without filtering - a VLAN separates traffic logically, but only becomes a security layer once a firewall or ACL restricts traffic between VLANs.
- Layers with the same weak spot - one admin account or the same password for every layer, or IT and OT accounts in the same domain. A single stolen account then opens every door.
- Prevention only, no detection - without monitoring nobody notices that a layer has already been breached, as with Stuxnet, which went unnoticed for a long time before it was discovered in 2010.
- Forgotten access routes - a supplier’s 4G modem or a permanent VPN connection that bypasses every layer.
- Paper layers - policy that exists but is never checked or exercised.
📏 How do you measure whether Defense in Depth works?
Defense in Depth only adds value if you can show that the layers actually work. Practical ways to measure it:
- Gap analysis per zone - compare the target security level (SL-T) with the achieved level (SL-A) according to IEC 62443-3-2 and IEC 62443-3-3.
- Walk through attack paths - take realistic scenarios from MITRE ATT&CK for ICS and check, step by step, which layer stops or detects the attack. A step without a layer is a gap.
- Testing - a penetration test or red team exercise shows whether layers hold up in practice, provided it is carefully planned around production.
- Tracking metrics - for example the share of assets in the inventory, the time to detect an incident, the number of open firewall rules and the share of critical patches installed or otherwise mitigated.
- Practising recovery - test periodically whether backups of PLC programs and servers can actually be restored.
For Dutch organisations covered by the Cyberbeveiligingswet, the Dutch implementation of NIS2 that has applied since 15 August 2026, this evidence is especially relevant. The law requires appropriate and proportionate measures for network and information systems, and a documented layered approach makes that duty of care demonstrable.
❓ Frequently asked questions
What does Defense in Depth mean?
Defense in Depth is a security principle in which multiple independent layers of controls are placed one behind the other. If one layer fails, the other layers still stop or flag the attack. The term originally comes from military strategy, where several lines of defence slow an attacker down.
How many layers does Defense in Depth have?
Defense in Depth has no fixed number of layers. NIST SP 800-82 Rev. 3 uses five (security management, physical, network, hardware and software), while other models list seven or eight layers. More important than the number is that the layers work independently and do not share the same weak spot.
Is a firewall enough for Defense in Depth?
A firewall on its own is not Defense in Depth, but one layer within that strategy. Defense in Depth also requires segmentation, hardening, access management, monitoring and an incident response plan, among other things. Relying on a single perimeter is exactly the mistake Defense in Depth is meant to prevent.
Is Defense in Depth mandatory under IEC 62443?
IEC 62443 uses Defense in Depth as a core principle, through zones, conduits and security levels among other things. IEC 62443-4-1 requires suppliers seeking certification to apply Defense in Depth in product design. For asset owners IEC 62443 is not a legal requirement in itself, but it is widely used to meet the NIS2 duty of care.
Does Zero Trust replace Defense in Depth?
Zero Trust does not replace Defense in Depth but strengthens its network and access layers. Zero Trust re-checks every access request regardless of network location. In OT environments with older PLCs, Defense in Depth with segmentation and monitoring remains necessary, because those devices do not support modern authentication.
How do I start with Defense in Depth in a plant?
A practical start to Defense in Depth in a plant is a complete inventory of OT assets and their connections, followed by a risk assessment per zone. The next steps are usually separating IT and OT with a DMZ, securing remote access through a jump server with MFA, and passive network monitoring. You then build up hardening and further segmentation step by step.
📌 In summary
Defense in Depth is the principle of multiple, independent and overlapping layers of security, each of which assumes that the previous one can fail. In OT environments it takes shape through IEC 62443 zones and conduits and the five layers of NIST SP 800-82: from policy and physical security to segmentation, hardening, monitoring and recovery. This limits the consequences of human error, vulnerabilities and attacks in both IT and OT.